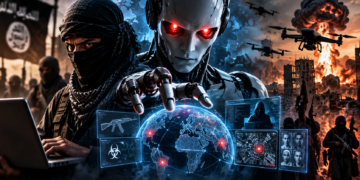
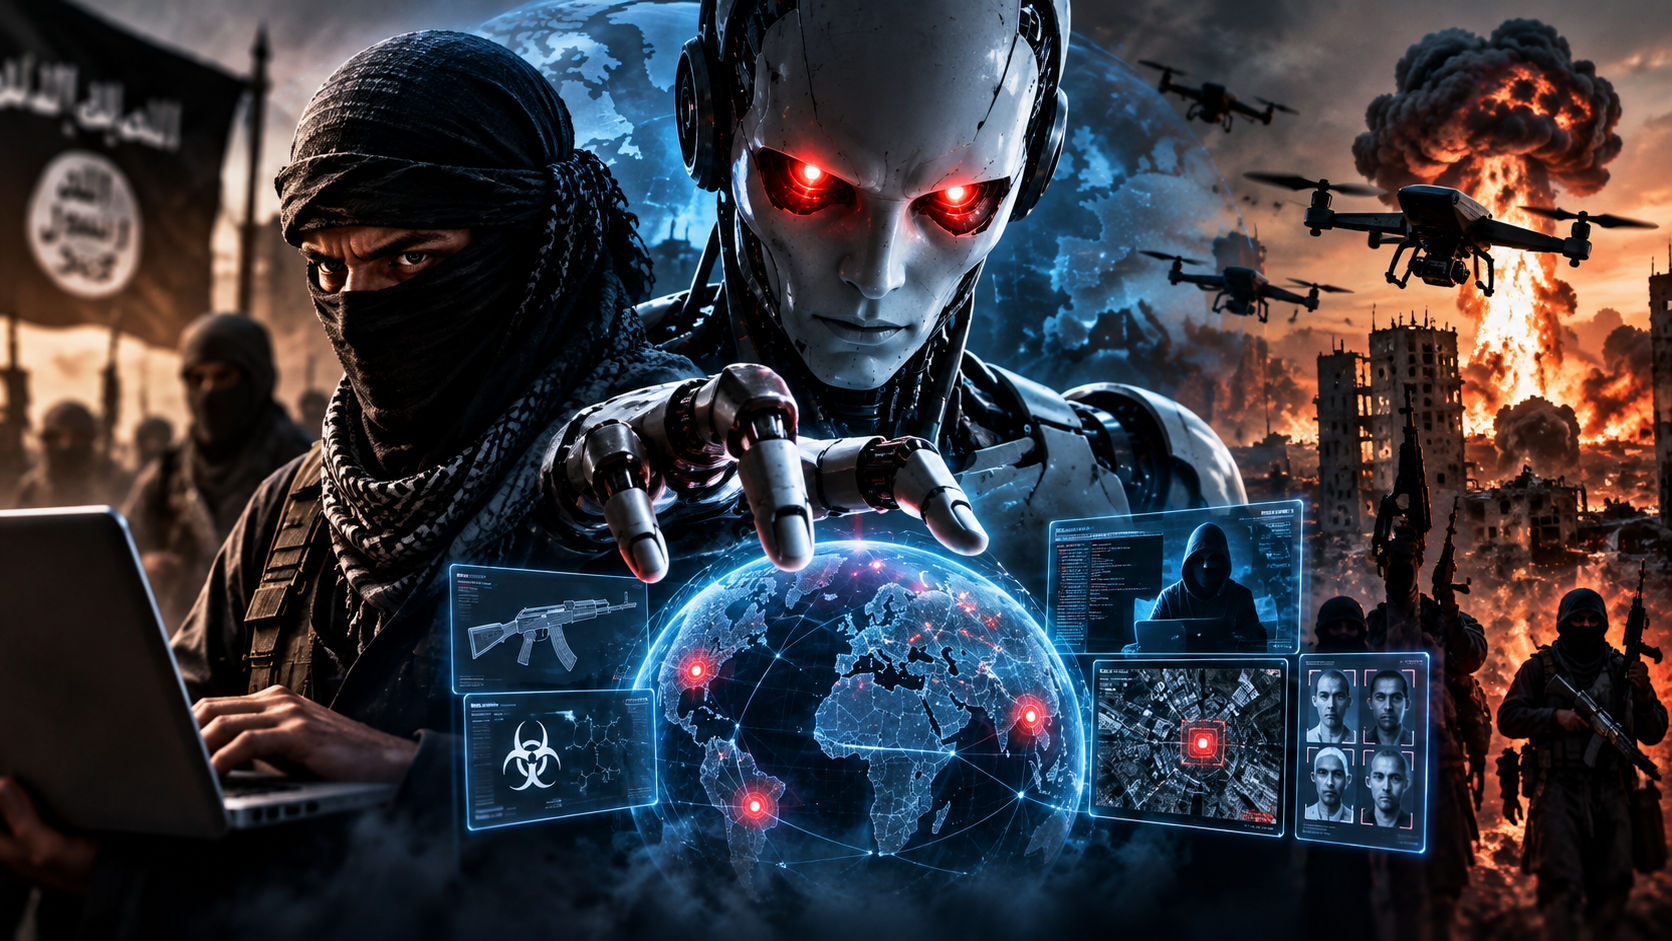
Terrorist organizations are beginning to exploit artificial intelligence as a practical tool for planning, weapons development, cyber operations and influence activity, raising a new forensic question: how much of the technology is actually changing the operational capabilities of violent groups and how much remains experimental?
Table of Contents
- The Warning Behind the Headline
- From Chatbot to Operational Tool
- The Yemen Case and the Weapons Question
- AI and the New Security Landscape
- Propaganda, Recruitment and Influence
- The Forensic Evidence Problem
- The Limits of AI Safeguards
- Why Terrorist Access Matters
- What Investigators Need to Establish
- The Next Battleground
The Warning Behind the Headline
A new warning about artificial intelligence is emerging from an uncomfortable place: not from a laboratory accident or a science-fiction scenario, but from documented attempts by violent and malicious actors to use commercially available AI systems. A CBS News report published this week examines how terrorist groups are taking advantage of advances in artificial intelligence, against the backdrop of growing concern among technology leaders and governments about the speed at which the technology is developing.
The report comes as Anthropic, the company behind the Claude family of AI models, has disclosed a series of cases in which threat actors attempted to use its systems for harmful purposes. The company’s September 2026 threat-intelligence report covers activity identified between December 2025 and August 2026 and describes misuse involving cyber operations, surveillance, influence operations, scams, biological research and conventional weapons development. Anthropic says it disrupted the activity and shared information with authorities and other industry partners where appropriate.
For investigators and national-security agencies, the significance is not simply that a terrorist or criminal can ask an AI system a dangerous question. The deeper issue is whether increasingly capable models can reduce the time, expertise and resources required to perform parts of an operation that once demanded specialist teams. The evidence does not show that AI has independently created a terrorist campaign. It shows that malicious actors are experimenting with AI as an additional operational capability.
From Chatbot to Operational Tool
The public image of generative AI is still dominated by writing, coding, image creation and research assistance. Security researchers, however, increasingly examine the same systems as dual-use technologies. A model that can explain an engineering problem, analyze large amounts of information or generate software can potentially be misused when a user applies those capabilities to an unlawful objective.
Anthropic’s latest threat report describes cases in which Claude was used across different stages of malicious activity. The company says the actors included suspected state-sponsored groups, financially motivated criminals, commercial spyware operators and politically motivated individuals. In the weapons category, Anthropic says it investigated six cases involving actors in China, Russia and Yemen who used or attempted to use Claude for weapons-related development or for intelligence gathering and procurement connected to weapons programs.
That does not mean the AI system simply supplied a finished weapon. The reported activity is better understood as augmentation: software that can help a person research, organize, reason through technical problems or accelerate portions of a larger project. This distinction matters because it changes the security question. Investigators are no longer looking only for an autonomous machine carrying out an attack. They must also consider a human operator using AI as a force multiplier while retaining responsibility for decisions and actions.
The Yemen Case and the Weapons Question
One of the cases highlighted by Anthropic involves a Yemen-based actor and conventional weapons development. Public reporting on the company’s disclosure has described the activity as an apparent effort connected to guided-missile development. Anthropic says its investigators detected and disrupted misuse involving weapons programs, while the broader report identifies Yemen as one of the locations associated with a weapons-development case.
The important forensic question is what the AI actually contributed. A conversation with a chatbot, by itself, is not evidence that a weapon was successfully designed, manufactured or deployed. Investigators would need to establish the identity of the users, authenticate the relevant records, determine what information was supplied by the model, and then trace whether those outputs were incorporated into physical or digital activity outside the AI platform.
That evidence chain is increasingly important as AI companies publish threat reports based on internal telemetry and investigations. Such reports can provide valuable intelligence, but they are not the same thing as a criminal conviction or an independently adjudicated finding. The cases describe detected behavior and the companies’ conclusions about it. Law-enforcement agencies would still need their own evidence if the activity became the basis for prosecution.
AI and the New Security Landscape
The CBS report places these developments within a broader debate about the dangers of rapidly advancing artificial intelligence. That debate has intensified as frontier models become capable of handling increasingly complex technical and analytical tasks. Anthropic published separate research in September measuring AI capabilities in tactical intelligence targeting and conventional weapons development, reporting that some models could perform tasks that historically required scarce, highly trained human expertise.
This is where the security implications become wider than terrorism alone. The same capabilities can potentially be used by states, criminal groups, intelligence operators, extremist networks or individual offenders. AI does not create the underlying motives. It can, however, alter the economics of carrying out an existing plan by making certain forms of research, analysis and content production faster or easier.
The effect is especially significant when a threat actor combines AI with existing infrastructure. An operator may already have access to stolen credentials, communication channels, technical equipment or specialist knowledge. AI can become another layer in that system. The danger therefore cannot be measured simply by asking whether a model can produce a dangerous answer. It also has to be measured by how the model interacts with tools, data, people and real-world systems.
Propaganda, Recruitment and Influence
Weapons development is only one part of the concern. AI can also be used in the information environment where terrorist organizations seek attention, recruit supporters and spread propaganda. Generative systems can produce text, translate material, create synthetic images or audio, and adapt messages for different audiences. These functions can lower the effort required to maintain a large and persistent online presence.
Researchers studying extremism have warned that AI-generated content can contribute to radicalization and propaganda ecosystems by increasing the speed and volume of material available to users. The technology can also complicate the work of investigators because synthetic media can blur the distinction between authentic recordings and fabricated material. A convincing image or video may attract attention long before its origin can be verified.
For counterterrorism agencies, this creates a two-sided problem. Analysts must identify genuine extremist activity while avoiding the mistake of treating every unusual or provocative AI-generated item as evidence of operational intent. Context, provenance and corroboration remain essential. A piece of propaganda can demonstrate ideological messaging without proving that an organization possesses the capability or intention to carry out the specific action depicted.
The Forensic Evidence Problem
The emerging AI threat also creates a new digital-forensics challenge. Investigators may have to reconstruct not just what an actor did, but how AI was incorporated into the process. That can require examining account records, prompts and outputs, application logs, API activity, device data, file histories and communications across multiple platforms.
The challenge is complicated by the fact that AI-generated material can be altered, copied or transferred outside the original platform. A document may have been produced by a model, edited by a human and then distributed through an encrypted messaging service. An image may be generated in one application and modified in another. By the time investigators obtain a file, the original creation history may no longer be obvious.
This is why authentication and chain of custody remain central. Investigators need to establish where a piece of evidence came from, whether it has been modified and how it relates to a suspect’s activity. In a criminal case, the existence of AI-generated material is only one part of the evidentiary picture. Prosecutors would still need to connect the material to a person, an intent and an unlawful act or attempt, depending on the relevant law.
The Limits of AI Safeguards
AI developers have responded to misuse concerns by building refusal systems, monitoring tools and classifiers designed to detect harmful requests. Anthropic says its threat-intelligence team actively investigates suspicious activity and uses lessons from those investigations to strengthen safeguards. The company says the cases in its September report were disrupted and that intelligence was shared with authorities and industry partners when appropriate.
But the very existence of these disclosures demonstrates the limits of preventive controls. Malicious users can change their language, split a task into smaller requests, use multiple accounts or combine several tools. Some may also turn to open-weight models or other systems that have different safety policies. Security therefore becomes an ongoing contest between model safeguards and attempts to bypass them.
Another complication is that safety is not identical across all AI systems. Anthropic’s own research notes differences among models, while the company’s transparency material describes continuing evaluations of capabilities in weapons-related and biological domains. As models become more capable, safeguards have to evolve with them. A policy designed around yesterday’s model may not be adequate for tomorrow’s system.
Why Terrorist Access Matters
Terrorist organizations have historically adapted commercially available technologies to their own purposes. The internet transformed propaganda and recruitment. Encrypted communications changed operational security. Consumer drones created new tactical possibilities. AI is now entering that same ecosystem as a general-purpose technology that can assist with language, information processing, software and media.
The significance is therefore less about a single chatbot and more about accessibility. If useful AI capabilities become inexpensive, widely available and easy to operate, the gap between highly resourced organizations and smaller groups can narrow in some areas. A group may not need to maintain a large internal technical department if external tools can perform portions of research or content production.
That does not mean AI automatically gives a terrorist organization sophisticated capabilities. Real-world operations still require people, logistics, physical resources, communications and opportunities. The technology can remove some friction, but it does not eliminate the other constraints. Security agencies will therefore have to distinguish genuine operational use from experimentation, propaganda or curiosity.
What Investigators Need to Establish
The central investigative task is attribution. When authorities discover a suspicious AI interaction, they need to determine who was behind the account, whether the account was compromised or shared, what the user was attempting to accomplish and whether the activity progressed beyond online experimentation. Those questions can require cooperation between technology companies, law enforcement and intelligence agencies.
Investigators also need to separate capability from intent. A person searching for information about a weapon is not necessarily preparing an attack. Conversely, a seemingly harmless request can become significant when combined with other evidence showing procurement, surveillance, recruitment or preparations for violence. The surrounding evidence often matters more than a single prompt.
This is one reason the latest disclosures should be read as warning signs rather than proof of a new era of autonomous terrorism. Anthropic’s cases show that malicious actors are testing what AI systems can do. They do not establish that terrorist groups can routinely conduct complex operations without human expertise. The evidence is strongest on experimentation and attempted misuse; the broader implications remain an active area of investigation.
The Next Battleground
The security landscape is moving toward a model in which AI becomes part of both the attack and the investigation. Malicious actors may use models to accelerate research, generate propaganda or support technical work. Investigators, meanwhile, will use AI-assisted tools to sift enormous datasets, identify patterns and connect digital evidence. The same technology can therefore become both an accelerant for offenders and an instrument for defenders.
That creates a race over evidence. Digital investigators will need methods capable of identifying synthetic content, preserving original records and reconstructing the sequence of human and machine actions. Courts may increasingly confront questions about whether an AI-generated document is authentic, whether a model’s output can establish intent, and how responsibility should be considered when a human uses an automated system to perform part of an unlawful task.
For now, the most concrete finding from the latest disclosures is straightforward: malicious actors are experimenting with advanced AI, and at least some attempts have involved serious security concerns including weapons development. The systems remain tools operated within human-directed campaigns, but their growing capabilities are changing what those tools can contribute. For counterterrorism and digital-forensics professionals, the task is no longer simply to monitor what people do online. It is to understand how human decisions and machine capabilities are becoming intertwined.
The CBS report therefore points to a problem that is likely to become increasingly important as frontier AI develops. The challenge is not simply preventing a chatbot from producing one dangerous answer. It is building a system of safeguards, intelligence sharing, digital forensics and law enforcement capable of detecting when AI assistance becomes part of a real-world threat. The distinction between experimentation and preparation may be difficult to draw, but it is precisely that distinction that investigators will increasingly have to prove.
ForensicTimes · forensictimes.com · Global Investigative Journalism on Crime, Justice, and Forensic Science · This report reflects verified open-source and wire reporting current as of publication. © 2026 ForensicTimes. All Rights Reserved.