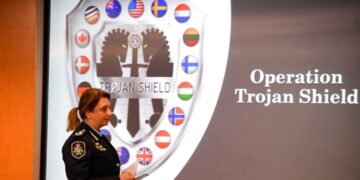
The latest international cyber operation exposed a criminal supply chain that is larger than any single hacking group. In November 2026, authorities working with Europol and Eurojust disrupted infrastructure associated with Gootloader, CastleRAT and StealC. The coordinated action involved 235 servers and 257 domains. Investigators identified more than 6 million stolen victim credentials in the targeted infrastructure, which criminals had used or intended to sell for further attacks, including ransomware.
The operation illustrates a defining feature of modern cybercrime: a victim may be targeted by one group, infected through a service operated by another, have credentials sold by a third party, and later face fraud or extortion from a separate criminal crew. These actors do not always operate under one name or command structure. They form a flexible economy in which access, malware, stolen information, infrastructure and money-laundering services can be bought, rented, exchanged or shared.
Stay Updated. Stay Alert. Stay Protected.
Read Forensic Times to stay informed about scams, fraud and emerging criminal threats. Explore scam and fraud warnings, crime-alert coverage, investigations into how criminals operate, and practical guidance to help protect your money, identity, family and business.