Her Work
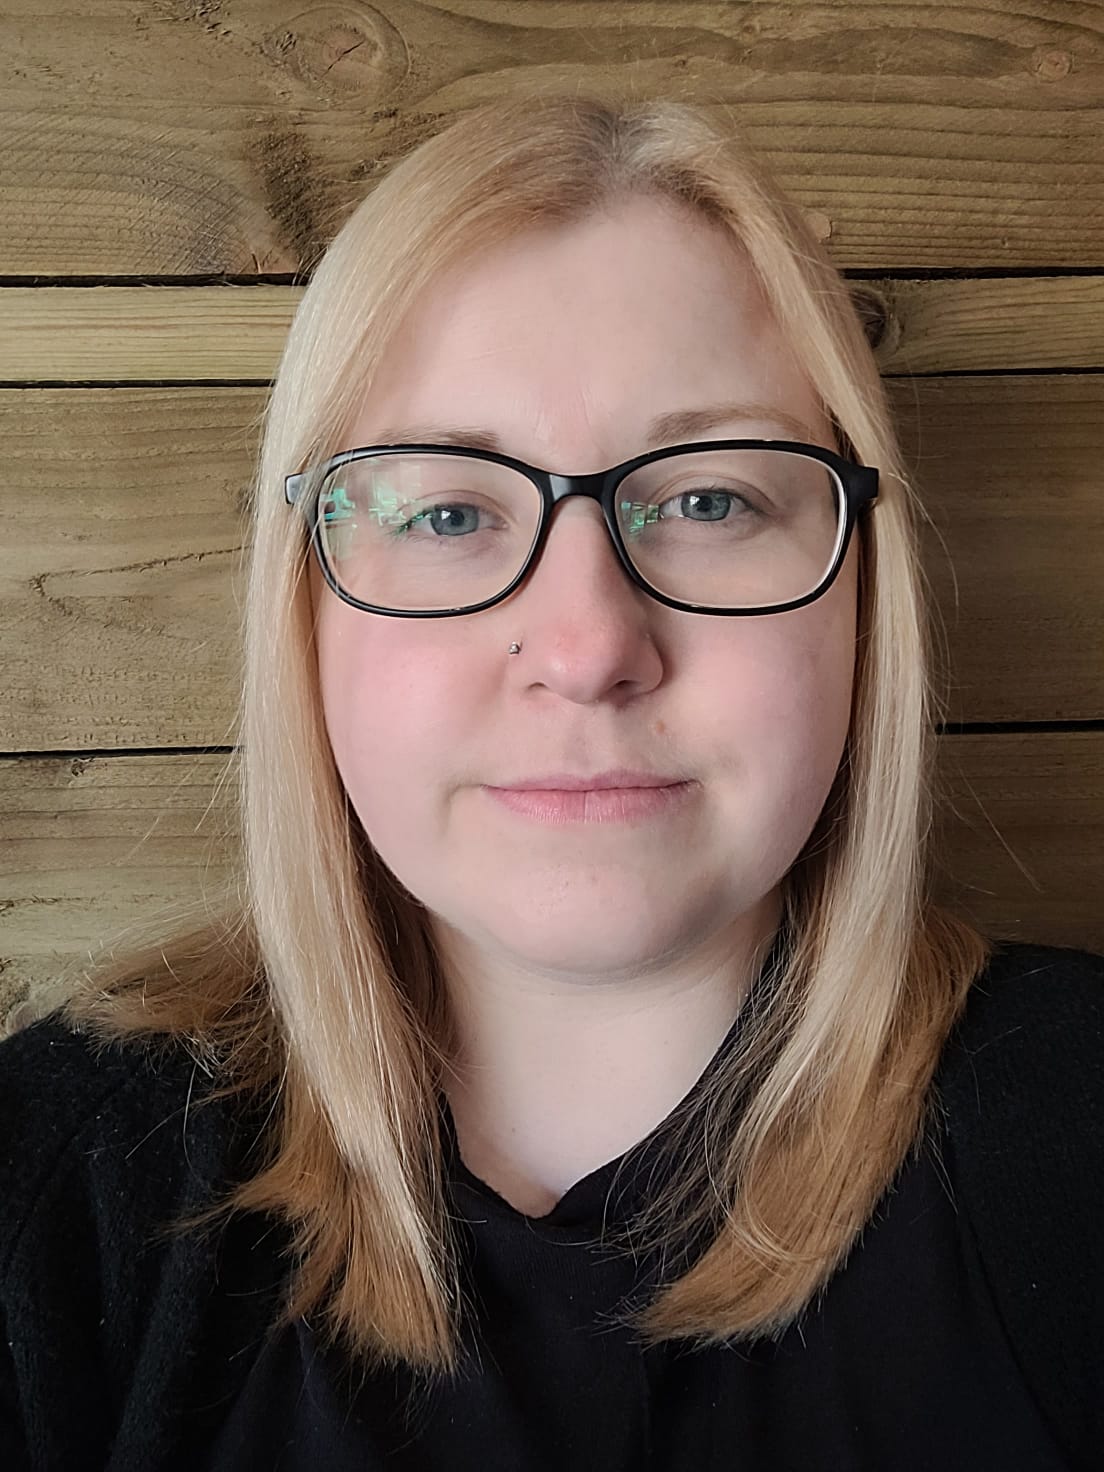
Rachael Medhurst is Course Leader of the MSc and BSc in Digital Forensics programme at the University of South Wales, where she has built her entire academic career — from BSc Forensic Computing through MSc Digital Forensics to her current PhD research in Digital Forensics and Incident Response within the Healthcare Sector. Her PhD examines DFIR capabilities in the UK healthcare industry in the context of the rapid proliferation of the Internet of Medical Things (IoMT) — a research agenda with direct implications for patient safety and national critical infrastructure resilience.
A Fellow of the Higher Education Academy (FHEA) with a PGCert in Learning and Teaching in Higher Education, Rachael combines deep technical expertise with a sophisticated understanding of forensic science pedagogy — designing and delivering modules in Mobile Forensics, IoT Forensics, Incident Response, Memory Forensics, and Malware Analysis. Her MSc final project explored Android Anti-Forensics vs Forensic Recovery; her undergraduate project investigated Steganography within Criminal Investigations.
Her practitioner credentials are extensive — Cellebrite Certified Operator, Magnet Certified Forensic Examiner (MCFE), Computer Hacking Forensic Investigator (CHFI), EC-Council Certified Incident Handler, Certified Threat Intelligence Analyst, Certified SOC Analyst, and ISO 27001 Lead Implementer — reflecting a commitment to operating at the cutting edge of digital forensic and cybersecurity practice.
Areas of Specialisation
Healthcare DFIR & IoMT Security
PhD research on Digital Forensics and Incident Response processes within the Healthcare Sector — specifically examining cyber-related attacks on medical devices and the DFIR capabilities available to UK healthcare organisations facing IoMT threats, with patient safety as the central consideration.
Mobile & IoT Forensics
Specialist expertise in mobile device forensics and IoT forensics — including Android anti-forensics and forensic recovery research, Cellebrite-certified mobile examination, and IoT device evidence acquisition and analysis across criminal and incident response contexts.
Malware Analysis & Memory Forensics
Deep expertise in malware analysis and memory forensics — the technical disciplines essential for understanding attacker tooling, lateral movement, persistence mechanisms, and post-compromise forensic artefacts in DFIR investigations.
Cyber Security & Forensic Education
Course Leader for MSc Applied Cyber Security at University of South Wales — module lead across Mobile Forensics, IoT Forensics, Memory Forensics, Malware Analysis, and Incident Response, with PGCert HE and FHEA fellowship underpinning a research-active, evidence-driven approach to curriculum design.
PhD & Academic Projects
DFIR in the Healthcare Sector — PhD Research
Advancing Digital Forensics and Incident Response Strategies Against Emerging Healthcare Cyber Threats — examining the DFIR capabilities of UK healthcare organisations in response to IoMT-specific attacks, with patient safety as the central constraint. University of South Wales, Oct 2023 – Sep 2029.
Android Anti-Forensics vs Forensic Recovery — MSc
MSc final project examining the tension between Android anti-forensic techniques — data deletion, encryption, wiping tools — and the forensic recovery capabilities available to investigators, with implications for mobile evidence admissibility and investigation methodology.
Steganography within Criminal Investigations — BSc
Undergraduate final project exposing the truth of steganography and its anti-forensic effects within criminal investigations — examining the detection, analysis, and evidentiary significance of hidden data in digital media.