Amman · Singapore · 13 MENA Countries · | ForensicTimes.com | Cybercrime · Human Trafficking · International Law Enforcement
Table of Contents
- The Announcement: 201 Arrests, Five Months of Operations
- Jordan: The Raid That Found Trafficking Victims Instead of Scammers
- Across the Region: What Each Country Found
- Forensic Analysis: How a 13-Country Cyber Operation Actually Coordinates
- The Private Sector Partners Who Made This Possible
- Criminal Psychology: Why Scam Centres Recruit Trafficking Victims
- Law and Legal Implications: Prosecuting Traffickers, Protecting Victims, Convicting Both
- Global Context: MENA’s Place in the Worldwide Scam Compound Economy
- Investigation: What Remains Unresolved
- Two Arrests, Fifteen Releases
The Announcement: 201 Arrests, Five Months of Operations
INTERPOL announced on May 18, 2026, from Singapore, that a coordinated cybercrime operation across the Middle East and North Africa had resulted in the arrest of 201 individuals, with a further 382 suspects identified for ongoing investigation. The operation, codenamed Ramz, ran from October 2025 through February 28, 2026, and involved thirteen countries: Algeria, Bahrain, Egypt, Iraq, Jordan, Lebanon, Libya, Morocco, Oman, Palestine, Qatar, Tunisia, and the United Arab Emirates.
INTERPOL described Operation Ramz as the first cyber operation of its scale coordinated by the organisation specifically within the MENA region — a characterisation that positions this action as a template-setting precedent rather than a routine enforcement exercise. The operation’s stated objectives were threefold: to investigate and disrupt malicious technical infrastructure, to identify and arrest suspects, and to prevent future financial losses. Over the course of the five-month operational window, participating countries disseminated nearly 8,000 pieces of crucial data and intelligence among each other to initiate and support individual national investigations — a volume of cross-border information sharing that itself represents a significant logistical and diplomatic achievement independent of the arrest figures.
The operation’s quantified results extended beyond arrests: 3,867 victims were identified across the participating countries, and 53 servers — the technical infrastructure underpinning the phishing, malware, and scam operations under investigation — were seized.
Jordan: The Raid That Found Trafficking Victims Instead of Scammers
Among the operational highlights INTERPOL specifically detailed, the case from Jordan stands apart in both its complexity and its implications. Jordanian police pinpointed the location of a computer being used to run financial fraud scams. The scheme operated through what appeared to be a legitimate trading platform: victims were persuaded to invest, and the platform shut down once funds had been deposited — a classic structure for what is commonly termed “pig butchering” fraud, in which victims are cultivated over time before being induced to make an investment that is never returned.
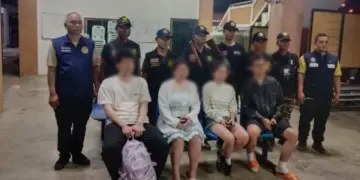
When Jordanian authorities raided the location running the scheme, they found 15 individuals carrying out the scam operations. Investigators determined, however, that these 15 people were not willing participants in the fraud but victims of human trafficking, recruited under false promises of legitimate employment from their home countries in Asia. Upon their arrival in Jordan, their passports were confiscated, and they were forced or coerced into participating in the scheme they had been brought there to run. Two individuals suspected of orchestrating the broader operation were arrested; the 15 trafficked workers were not treated as criminal suspects but as the victims their circumstances established them to be.
Across the Region: What Each Country Found

INTERPOL’s account of Operation Ramz documents specific operational outcomes from five of the thirteen participating countries, each illustrating a distinct facet of the broader cybercrime threat landscape the operation was designed to address.
In Qatar, intelligence obtained through the operation led to the identification of compromised devices whose unsuspecting owners were themselves victims of cyberattacks, unaware that their devices were being used to spread malicious threats to other targets — a pattern consistent with botnet-style exploitation, in which legitimate users’ devices are conscripted, without their knowledge, into the infrastructure of a broader attack. The affected systems were secured and their owners notified to take preventive measures, reflecting a victim-support dimension to the operation that extended beyond the headline arrest figures.
In Oman, investigators identified a server in a private residence containing sensitive information. The server’s owner had legitimate access to that information, but the server itself suffered from multiple critical security vulnerabilities, including malware infection — a case illustrating how legitimate infrastructure can become an unwitting vector for broader criminal exploitation through inadequate security practices rather than any deliberate wrongdoing by the asset’s owner. Authorities took action to disable the server and prevent further harm.
In Algeria, a website offering “phishing as a service” — a commercial model in which phishing infrastructure, templates, and tools are sold or rented to other criminal actors rather than used directly by the infrastructure’s operators — was identified and dismantled. Authorities located and seized the suspicious server along with a computer, a mobile phone, and hard drives containing phishing software and scripts. One suspect was taken into custody.
In Morocco, authorities seized computers, smartphones, and external hard drives containing banking data and software used for phishing operations. Three individuals are now undergoing judicial procedures as a result, with others remaining under investigation.
Forensic Analysis: How a 13-Country Cyber Operation Actually Coordinates
The forensic and operational architecture underlying Operation Ramz illustrates the specific mechanics by which a multinational cybercrime operation of this scale is technically and procedurally coordinated. The nearly 8,000 pieces of data and intelligence disseminated among participating countries represent the connective tissue that allowed thirteen separate national law enforcement systems, each operating under its own domestic legal framework and investigative procedures, to function as components of a single coordinated effort rather than thirteen unconnected national investigations.
The 53 seized servers represent the physical and digital infrastructure layer of the investigation — the actual computing resources used to host phishing pages, distribute malware, manage stolen banking data, and operate the fraudulent platforms documented in the Jordan, Algeria, and Morocco cases specifically. Server seizure in cybercrime investigations serves both an evidentiary function, preserving logs, code, and configuration data that establish how the criminal infrastructure operated and who controlled it, and a disruptive function, immediately removing the technical capability to continue the criminal activity regardless of how long the subsequent legal proceedings against any individual suspect take to conclude.
The identification of 3,867 victims across the operation’s duration reflects a parallel and distinct forensic process from the infrastructure-seizure and suspect-identification work: victim identification in cybercrime cases of this kind typically depends on financial transaction tracing (following the money from a victim’s bank account or cryptocurrency wallet to the criminal infrastructure), platform and communication record analysis (identifying who interacted with a given phishing site or fraudulent platform), and, in cases like the compromised devices identified in Qatar, direct technical analysis of malware-infected systems to determine whose devices were affected and notify them accordingly.
The Private Sector Partners Who Made This Possible
INTERPOL explicitly credited a specific set of private-sector cybersecurity partners as essential collaborators in Operation Ramz: Group-IB, Kaspersky, the Shadowserver Foundation, Team Cymru, and TrendAI. This partnership structure reflects a now well-established and increasingly necessary model in international cybercrime enforcement, in which national and international law enforcement agencies — which possess arrest powers, judicial authority, and cross-border legal cooperation mechanisms but frequently lack the specialised technical capacity to independently track sophisticated criminal infrastructure at scale — partner with private cybersecurity firms and non-profit threat intelligence organisations that possess exactly that specialised technical tracking capacity but no independent enforcement authority of their own.
Group-IB and Kaspersky are commercial threat intelligence and cybersecurity firms with extensive global visibility into malware campaigns, phishing infrastructure, and criminal hosting patterns, accumulated through their core commercial cybersecurity product operations. The Shadowserver Foundation and Team Cymru are non-profit threat intelligence organisations specifically oriented toward supporting law enforcement and the broader cybersecurity community with malicious infrastructure tracking and takedown support, operating on a model that prioritises public-interest threat disruption over commercial sale of their intelligence capabilities. This combination of commercial and non-profit private partners working alongside INTERPOL and thirteen national police forces represents the kind of hybrid public-private enforcement coalition that contemporary cybercrime — which routinely operates across borders that conventional law enforcement jurisdiction does not — increasingly requires to achieve meaningful disruption.
Criminal Psychology: Why Scam Centres Recruit Trafficking Victims
The Jordan case’s revelation that 15 individuals running a fraudulent trading platform scam were themselves trafficking victims rather than willing perpetrators reflects an operational logic that has become increasingly well documented across the global scam compound economy, particularly in but not exclusive to Southeast Asia, where the pattern was first extensively reported and investigated.
Scam operation organisers face a specific labour problem: running convincing, sustained fraud schemes — particularly relationship-based investment fraud of the kind documented in the Jordan case, which requires patient, ongoing communication with victims over extended periods to build the trust necessary for eventual investment — requires a substantial and reliable workforce willing to spend long hours engaged in psychologically demanding, ethically compromised labour. Trafficked workers, recruited under false employment pretences and then stripped of their passports and freedom of movement upon arrival, solve this labour problem in a manner that voluntary employees, who retain the freedom to quit when the work’s true nature becomes apparent, cannot: trafficked workers cannot leave, cannot report the operation to authorities without risking their own prosecution or harm, and can be coerced into sustained, high-volume fraud labour for as long as their traffickers control their documents and movement.
This operational model creates the specific evidentiary and legal complexity that confronted Jordanian investigators directly: the individuals physically operating the fraud — the ones a surface-level raid would identify as the scammers — were simultaneously victims of a separate and prior crime (trafficking) being compelled to commit the crime investigators were originally seeking to prosecute (fraud). Distinguishing between the orchestrators (the two individuals arrested) and the coerced labour (the 15 individuals identified as trafficking victims) required investigators to look beyond the immediate fact of who was operating the computers and establish the coercive context that determined each individual’s actual culpability.
Law and Legal Implications: Prosecuting Traffickers, Protecting Victims, Convicting Both
The legal framework applied in the Jordan case reflects an increasingly standard approach in international anti-trafficking law and practice, embodied in the United Nations Trafficking Protocol’s non-punishment principle: victims of trafficking should not be held criminally liable for unlawful acts they were compelled to commit as a direct consequence of their trafficking situation. Jordanian authorities’ decision to arrest only the two individuals identified as the operation’s orchestrators, while treating the 15 individuals who physically ran the scam communications as trafficking victims rather than fraud suspects, directly applies this principle.
The orchestrators face prosecution under Jordan’s anti-trafficking and cybercrime statutes simultaneously — the trafficking charges addressing their role in recruiting, transporting, confiscating documents from, and coercing the 15 victims, and separate fraud and cybercrime charges addressing the underlying scam operation itself, which caused direct financial harm to the scheme’s actual victims, the people who invested in the fraudulent trading platform. This dual-track prosecution reflects the layered nature of the crime: a trafficking offence (against the 15 coerced workers) operating in service of a separate fraud offence (against the platform’s investment victims), with the same two orchestrating individuals bearing criminal responsibility for both layers.
Across the broader operation, the range of charges and judicial outcomes described — Algeria’s single suspect in custody, Morocco’s three individuals undergoing judicial procedures, the ongoing investigation of the 382 additional identified suspects — reflects the standard reality of large-scale, multinational cybercrime operations: the headline arrest number represents a range of legal outcomes still working through thirteen distinct national judicial systems, each with its own pace, evidentiary standards, and sentencing frameworks for cybercrime and trafficking offences.
Global Context: MENA’s Place in the Worldwide Scam Compound Economy
The trafficking pattern uncovered in Jordan during Operation Ramz situates the MENA region within a documented global phenomenon that has, until now, been most extensively reported in the context of Southeast Asia’s Myanmar-Cambodia-Laos scam compound network — the same broader criminal ecosystem covered in ForensicTimes’ prior reporting on Chinese nationals trafficked toward Myanmar border compounds. The Jordan case demonstrates that the underlying business model — recruit workers from one region under false employment pretences, transport them across borders, confiscate their documents, and coerce them into running scam operations targeting victims in third countries — is not geographically confined to Southeast Asia but represents a transferable criminal methodology that has now been documented operating within the Middle East as well.
This geographic expansion has specific implications for international anti-trafficking and cybercrime cooperation. The European Union and the Council of Europe’s partial funding of Operation Ramz, channelled through the CyberSouth+ project specifically designed to build cybercrime investigative capacity across North Africa and the broader Mediterranean and Middle East region, reflects a recognition among European institutions that cybercrime infrastructure operating from or through the MENA region poses a direct threat to European citizens and financial systems, given the inherently borderless nature of phishing, malware distribution, and online fraud. Qatar’s Ministry of Interior’s direct operational support for the operation similarly reflects Gulf state recognition that the region’s growing digital economy and financial infrastructure makes it both a target for and, as the Jordan case demonstrates, a potential operational base for transnational cybercrime and associated trafficking.
Investigation: What Remains Unresolved
The current status, location, and support arrangements provided to the 15 trafficking victims identified in the Jordan raid have not been detailed in INTERPOL’s public announcement. Whether they have been granted any form of immigration relief, victim support services, or assistance returning to their home countries in Asia, and whether they have provided testimony that might assist in identifying or prosecuting the broader network beyond the two individuals already arrested, is not addressed in available reporting.
The identities, nationalities, and recruitment pathways of the 15 trafficked individuals — including which specific countries in Asia they were recruited from, and what employment they believed they were travelling to Jordan to perform — have not been disclosed, consistent with standard victim confidentiality practice in trafficking cases.
The status of the 382 additional suspects identified but not yet arrested across the thirteen participating countries, and the timeline for any further enforcement action against them, has not been detailed. Whether any of those 382 suspects are connected to the Jordan trafficking-linked scam operation specifically, or to entirely separate phishing, malware, or fraud infrastructure uncovered elsewhere in the operation, is not addressed in current public reporting.
The full financial scale of losses connected to the 3,867 identified victims across all thirteen countries has not been quantified in INTERPOL’s public statement, which provides victim and arrest counts but no aggregate financial damage figure comparable to the kind of total-loss reporting seen in other major cybercrime operations.
Two Arrests, Fifteen Releases
Operation Ramz will likely be remembered, in the institutional record INTERPOL keeps of its own work, primarily for its scale: 201 arrests, 382 additional suspects identified, 3,867 victims found, 53 servers seized, thirteen countries coordinated for the first time at this magnitude in the MENA region. Those numbers describe a genuine and significant law enforcement achievement.
What they do not immediately convey is what Jordanian investigators found when they actually opened the door on one specific fraud operation: not a room full of scammers to arrest, but 15 people whose passports had been taken from them, who had been promised one kind of life and delivered into another, and who were running a fraud scheme not because they chose to but because the people who trafficked them had made any other choice impossible. Two men were arrested for that. Fifteen people were, in the same raid, finally allowed to stop.
ForensicTimes · forensictimes.com · Investigative Journalism on Crime, Justice & Forensic Science · © 2026 ForensicTimes. All rights reserved.